Companies now produce unprecedented volumes of data. Business documents, compliance evidence, operational data, application histories, AI-generated content, security logs, audit reports, and regulatory archives are growing in volume and importance, and becoming more sensitive.
Yet, most storage infrastructures continue to be designed according to a simple logic: store, back up, restore. This approach was sufficient for a long time. It no longer is.
Cyberattacks are increasing. Regulatory requirements are tightening. Organisations must demonstrate their compliance, auditors demand evidence, and teams must understand what happened several months after an incident.
The real question is therefore no longer just:
Where is my data?
But rather:
Can I prove its integrity, retrieve its history, and revert exactly to the desired state?
This challenge prompted Challenges to cover KARL.
A new approach to storage
The Challenges article presents a different approach to data storage: preserving not only files but also their history — every modification, version, evolution, and system state.
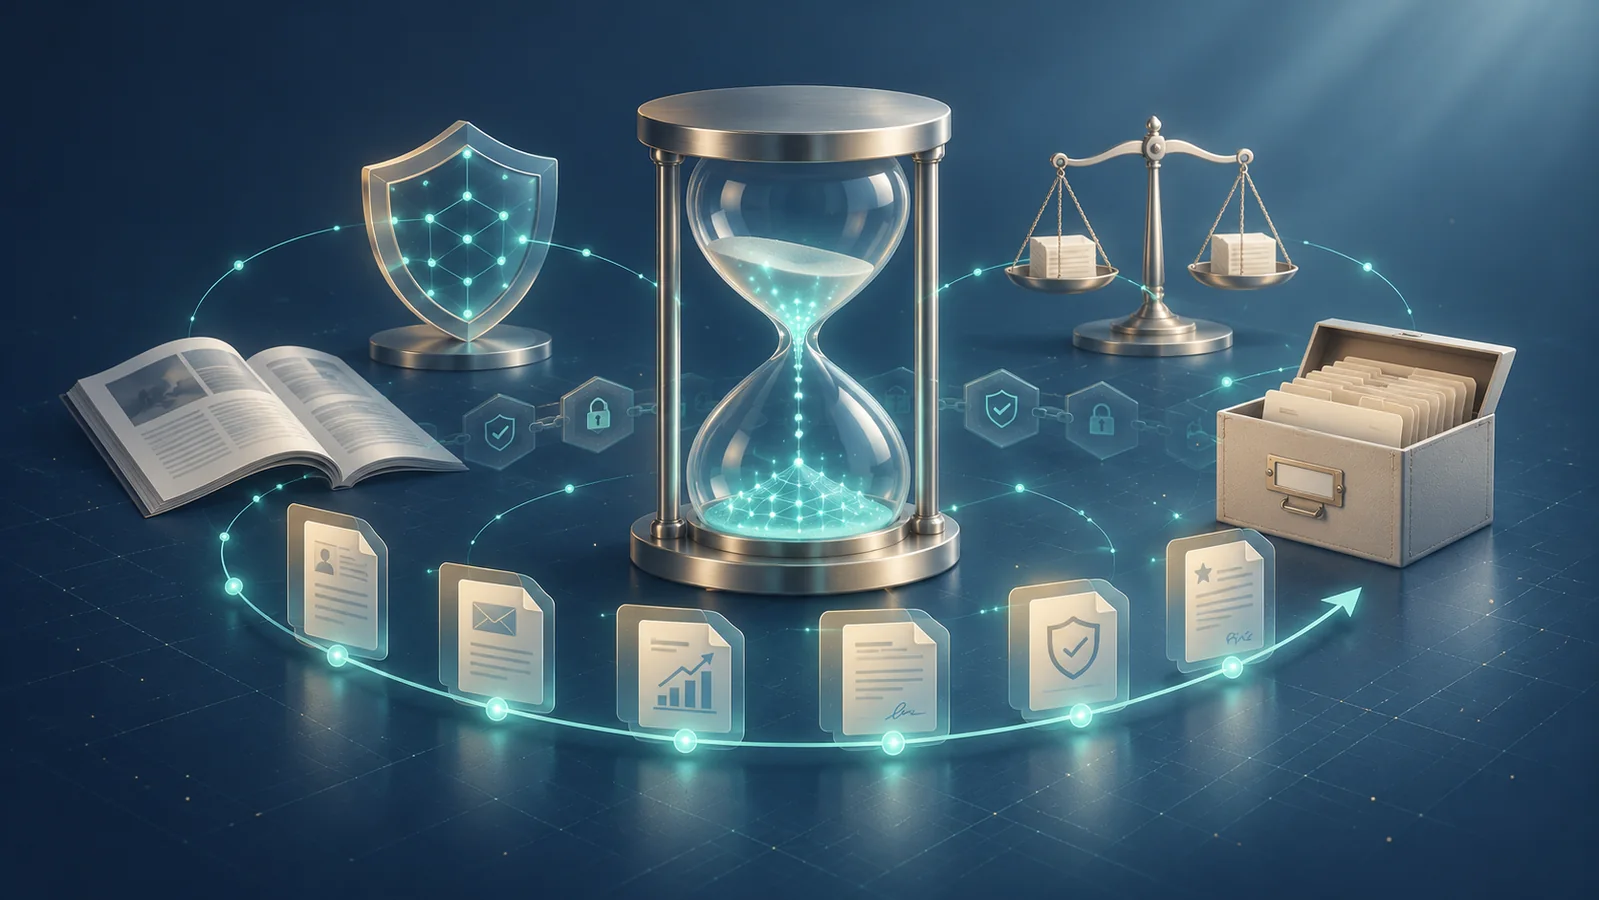
KARL thus introduces the concept of documentary memory. Data is no longer merely stored: it becomes observable over time.
This approach specifically enables:
- exploring the complete history of a document;
- reverting to a precise moment in time;
- comparing multiple versions;
- to quickly restore a previous state;
- to have complete traceability.
Resilience against cyberattacks
No organisation can guarantee that it will never be attacked. Even the best-protected environments can fall victim to:
- ransomware;
- human error;
- mismanagement;
- software corruption;
- an internal malicious act.
In this context, the question becomes:
Are we capable of quickly returning to a healthy state?
KARL addresses this issue through its temporal approach. Organisations have a documentary time-navigation capability allowing them to precisely identify, understand and restore the state preceding an incident.
Addressing compliance challenges
Modern regulations impose increasingly stringent requirements: NIS2, GDPR, MiFID II, SEC 17a-4, eIDAS, ISO 27001, DORA. All share a common need: the ability to demonstrate compliance.
Companies must be able to produce:
- evidence;
- reports;
- logs;
- histories;
- attestations;
- audit trails.
KARL was designed to address these challenges by transforming documents and their evolutions into auditable, historised, and traceable assets. The objective is not merely to preserve information: it is to be able to defend it before an auditor, a regulator, or a client.
The emergence of corporate digital memory
The article also highlights a profound shift in how organisations manage their knowledge. For years, storage systems were designed as preservation spaces. In the future, they must become spaces for understanding.
Companies now seek to:
- understand past decisions;
- retrieve the elements that led to a specific action;
- analyse the evolution of a document;
- reconstruct context;
- feed reliable artificial intelligence systems.
This digital memory is progressively becoming a strategic asset, and KARL is fully aligned with this evolution.
Why this article is important
The Challenges article highlights an often underestimated issue: the role of time in data.
While the market generally focuses on storage capacity, performance, or cost, KARL introduces a new dimension: the temporal continuity of information.
This approach is particularly of interest to:
- CISOs;
- CIOs;
- compliance teams;
- auditors;
- hosting providers;
- cloud operators;
- organisations subject to stringent regulatory requirements.
Read the full article
The full article published by Challenges is available here:
Read the article on Challenges →
Discover KARL
Would you like to learn more about how KARL enables the creation of a resilient, traceable, and auditable documentary archive over time? Contact us for a demonstration or a personalised presentation.