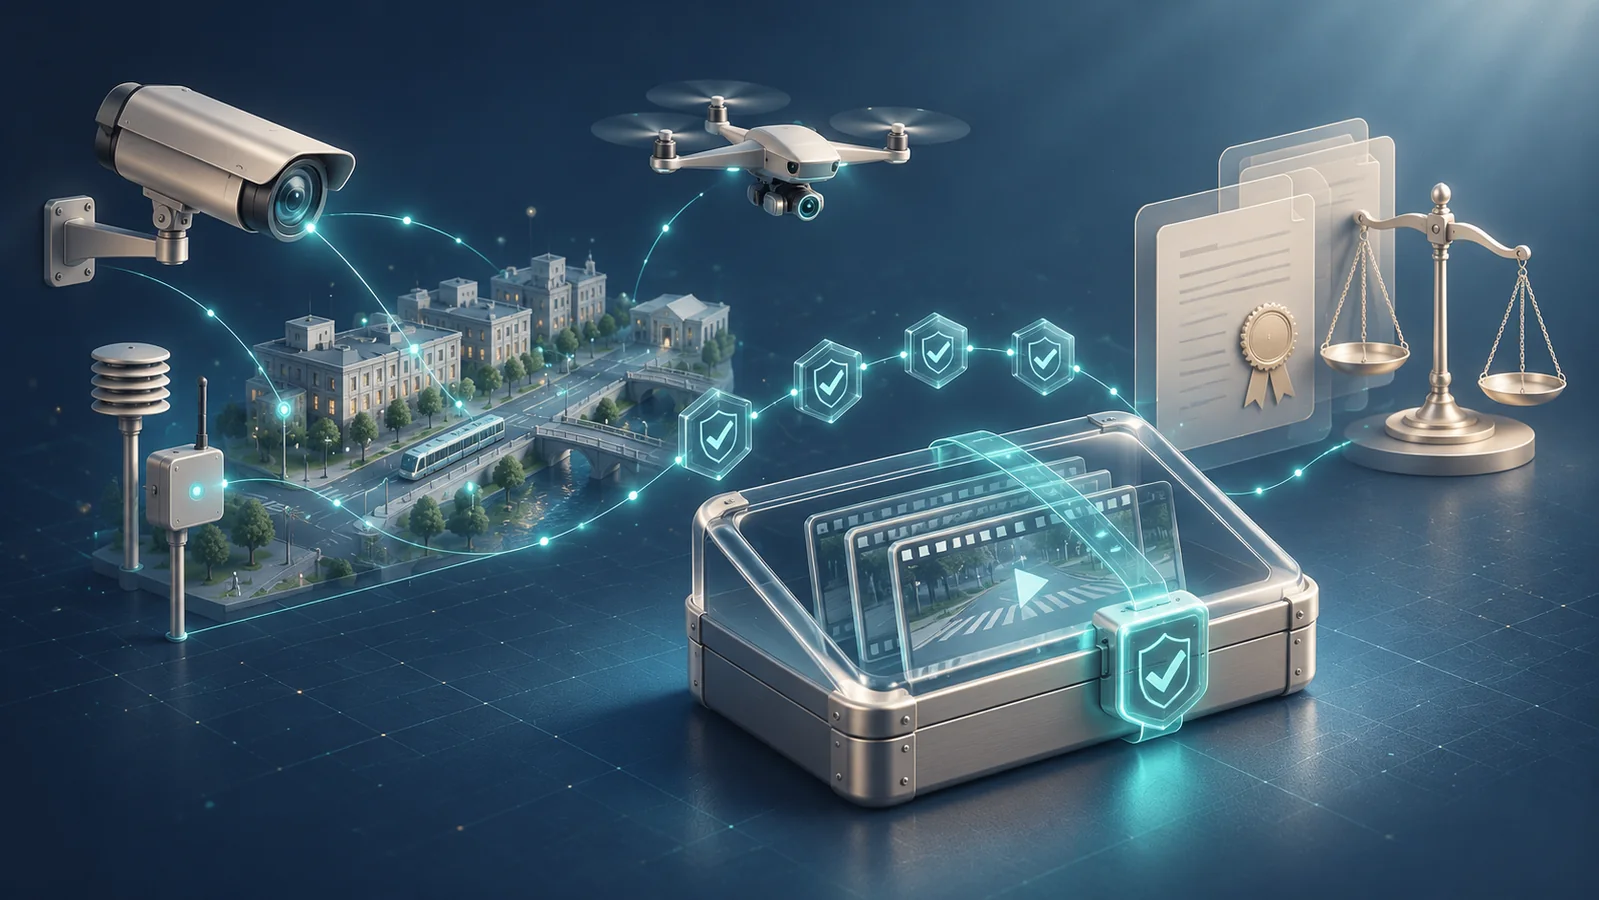
Surveillance cameras, autonomous drones and IoT sensors are creating more sources of recorded data. Video may be used as evidence in civil or criminal proceedings, but its probative value depends on traceable provenance, integrity during storage and compliance with legal requirements (GDPR, laws of evidence). Organisations must address these technical, regulatory and operational requirements before integrating the sources into their information systems.
Introduction – The need for trust at the heart of the digital shift
Imagine a city where every public square is equipped with high-resolution cameras, every industrial plot monitored by drones in continuous flight, and every warehouse fitted with IoT sensors detecting movement and incidents. In the event of an accident, burglary, or legal dispute, authorities request to see the recordings: these then constitute the 'evidence' that could sway the judgment.
However, French case law (Cass. crim., 13 May 2022) reminds us that for an image to be admissible, it must be demonstrated:
- Authenticity: the recording has not been altered.
- Chain of custody: every transfer has been logged and secured.
- Compliance with fundamental rights (privacy, proportionality).
These requirements rely on a reliable technical architecture, rigorous process management, and precise legal compliance. The convergence of traditional video surveillance, autonomous drones, and connected objects creates new points of vulnerability: saturated bandwidth, dispersed storage, uncontrolled software updates, or the abusive exploitation of metadata.
In the following sections, we detail the technological levers (cryptography, timestamping, logging), regulatory frameworks (GDPR, NIS2, ISO/IEC 27037 standards), and integration best practices so that every organisation can transform its video streams into admissible evidence while managing risks.
1 Legal framework and evidentiary requirements
| Domain | Main reference frameworks | Implications for the chain of trust |
|---|---|---|
| Protection of personal data | GDPR (Art. 5, 32), LIL (France) | Encryption at rest & in transit, metadata minimisation, processing register |
| Digital evidence | Civil Code Art. 1316-1, case law Cass. 13/05/2022, ISO/IEC 27037 | Reliable timestamping, full traceability, eIDAS-compliant electronic signature |
| Information systems security | NIST SP 800-53 (AU-3, SC-12), ENISA "Guidelines on Video Surveillance" | Strict access controls, immutable logging, DDoS attack resilience |
Key points
- Qualified timestamping – Under the eIDAS regulation, a qualified trust service provider for timestamps (QTSA) ensures that data has not been altered after creation.
- Consent and lawfulness of processing – GDPR requires a legal basis (public security, legitimate interest) and, where possible, notifying individuals being filmed via signage.
- Retention period – CNIL recommends 30 days for video surveillance in public spaces, unless specifically justified (e.g., an investigation).
2 Technical architecture of a video chain of trust
2.1 Capture-to-storage workflow
[Caméra / Drone / Capteur IoT] → Edge Gateway → Transport sécurisé (TLS‑1.3) → Object Store chiffré → Service d’horodatage qualifié → Archive immuable- Edge gateway: aggregates streams, applies AES-256 GCM encryption prior to transmission, and adds integrity metadata (HMAC-SHA-256).
- Secure transport – TLS 1.3 minimises latency while ensuring mutual authentication of endpoints (X.509 certificates).
- Encrypted Object Store – S3 compatible solutions with SSE-KMS, enabling Attribute-Based Access Control (ABAC).
2.2 Timestamping and digital signature
- The encrypted stream is sent to an eIDAS certified Trusted Timestamp Authority (TSA) service.
- The TSA returns a token containing the file hash, the timestamp, and its digital signature.
- This token is stored with the video in an immutable archiving layer (e.g., WORM – Write-Once-Read-Many).
2.3 Tamper-proof logging
- Use of logging systems based on private blockchain or Merkle trees to guarantee the integrity of access and modification records.
- Each entry includes: actor identity, timestamp, action (read, copy, delete), and the hash of the relevant file.
2.4 Resilience & Availability
| Risk | Mitigation Mechanism |
|---|---|
| Bandwidth loss (e.g., rural areas) | Adaptive bitrate H.265 compression, edge temporary storage until reconnection |
| TSA failure | Multi-TSA redundancy with quorum (2/3 signatures required) |
| Storage corruption | Geo-dispersed replication + periodic checksums (SHA-512) |
3 Identity and Access Management (IAM) for video streams
- Principle of Least Privilege – Security operators only have access to cameras within their assigned perimeter.
- Strong authentication – Mandatory MFA, ideally via client certificates or FIDO2.
- Role-Based Access Control (RBAC): ROLE_SV_ADMIN, ROLE_DRONE_OP, ROLE_IOT_MAINTENANCE. Each role is assigned a policy set defining the permitted actions on the S3 bucket (s3:GetObject, s3:PutObjectTagging).
- Continuous Auditing – Integration with SIEM (e.g., Elastic Stack) to correlate access logs with security incidents.
4 Data Protection and GDPR Compliance
4.1 Minimisation & Pseudonymisation
- GPS metadata or personally identifiable information (number plate, face) is pseudonymised at the point of capture via an ISO/IEC 20546 certified AI blurring module.
- The storage of personally identifiable information (PII) is limited to the 30 days required for investigation purposes.
4.2 Consent Management and Public Information
- Signage displaying a GDPR-compliant privacy notice with a QR code linking to the video surveillance policy.
- Logging of access or erasure requests (right to be forgotten) within the same immutable log system, providing proof of compliance during a CNIL audit.
4.3 Impact on Fundamental Rights
- A Data Protection Impact Assessment (DPIA) is mandatory whenever a camera covers a private area (e.g., an inner courtyard).
- The DPIA must be reviewed annually or in the event of a substantial modification to the system (new drone, software update).
5 Drone and IoT Sensor Security
| Element | Primary Threat | Recommended Countermeasure |
|---|---|---|
| Flight Control (drone) | Hijacking via protocol: unencrypted MAVLink | Use MAVLink 2 with AES-128 encryption and mutual authentication |
| Firmware | Malicious code injection during OTA updates | Firmware digital signatures, validation via Secure Boot |
| Radio Communication | Interception of video streams over Wi-Fi/5GHz | Migration to LTE-Advanced Pro network with site-to-site IPSec VPN |
| IoT sensors | Botnet (e.g., Mirai) exploiting open ports | Disabling unnecessary services, VLAN segmentation + strict ACLs |
5.1 Lifecycle Management
- Provisioning – Each device receives a unique X.509 certificate during manufacturing (internal PKI).
- Secure Update – Signed OTA server, integrity verification prior to flashing.
- Decommissioning – Immediate certificate revocation and purging of keys stored in the HSM.
6 Use Case: criminal investigation into an industrial site burglary
- Capture – Three fixed cameras, two patrol drones, and twenty IoT sensors (glass break detection) simultaneously record the incident.
- Transmission – Streams are encrypted in real-time and sent to the site's edge gateway.
- Timestamping – Each video fragment receives a QTSA token, stored in the WORM archive.
- AI Analysis – An intrusion detection engine (ISO/IEC 2382-37 compliant) identifies faces and generates pseudonymised metadata.
- Chain of custody – The SIEM logs every access by the forensic investigator: read, export, print.
- Evidence production – In court, the lawyer presents the video file accompanied by the QTSA token and the TSA-signed access log, thereby proving the integrity and timestamping of the events.
Lessons learned
- The qualified signature successfully overcame objections regarding the potential alteration of images.
- Network segmentation limited the risk of compromise during the investigation phase (no leaks to the Internet).
- Pseudonymisation satisfied the defence regarding compliance with image rights, while maintaining probative relevance.
7 Points of vigilance
Major risks and mitigation measures
| Risk | Potential consequence | Mitigation measure |
|---|---|---|
| Post-capture tampering | Loss of probative value, legal sanctions | Qualified timestamping + WORM storage |
| Privacy breach | CNIL action, fines up to 4% of turnover | Prior DPIA, AI blurring, information signage |
| TSA failure | Invalidation of timestamps | Multi-TSA redundancy with quorum |
| Drone compromise | Unauthorised dissemination of sensitive images | Mutual authentication, stream encryption, signed firmware |
| Excessive retention | GDPR non-compliance | Automated purge policy based on legal metadata |
8 Operational decisions for organisations
| Decision | Key question | Concrete recommendation |
|---|---|---|
| Storage selection | Should public cloud or on-premise infrastructure be prioritised? | Opt for a hybrid approach: critical data (evidence) in the Cloud with ISO/IEC 27001 compliance certification, local WORM archiving for sovereignty. |
| Key management | Who controls the KMS and how can a “single point of failure” be avoided? | Use a redundant HSM (e.g., AWS CloudHSM + on-premise Thales) with separation of duties (CIO vs CISO). |
| TSA Selection | Is the provider eIDAS certified and does it offer a REST API? | Select a qualified provider (e.g., DigiCert, GlobalSign) with an SLA < 1ms latency for high-frequency video streams. |
| AI Integration | Is facial recognition legal within our jurisdiction? | Conduct a legal impact assessment and restrict usage to public areas explicitly covered by legislation. |
| Continuity Plan | How can the availability of evidence be ensured in the event of a disaster? | Implement geo-dispersed replication + regular restoration tests (RTO < 4h, RPO < 15min). |
9 Operational Conclusion
The probative value of an image no longer depends solely on the legal framework but also – and above all – on the technical robustness of the chain of trust supporting it. By combining end-to-end encryption, qualified timestamping, immutable logging, and rigorous access governance, organisations can leverage video surveillance, drones, and IoT as reliable sources of evidence while complying with GDPR requirements and civil society expectations.
However, these benefits come with associated costs (HSM infrastructure, TSA licences, DevSecOps expertise) and increased responsibilities (DPIA, incident management). The decision to invest must therefore be based on a detailed cost-benefit analysis, the steering of organisational maturity, and the anticipation of regulatory changes (e.g., NIS2 directive).
By following the best practices outlined above, every stakeholder – from executives to security engineers – will be able to transform their video streams into legally admissible evidence, resilient against cyber threats and compliant with data protection requirements.
Key takeaways for decision-makers
- Authenticity & timestamping: only a qualified signature guarantees probative value.
- Immutable chain of custody: logs based on Merkle trees or private blockchain prevent any contestation.
- GDPR compliance: DPIA, minimisation, and public notification are mandatory from the outset.
- Endpoint security (cameras, drones, sensors): encryption, signed firmware, and mutual authentication are indispensable.
- Hybrid architecture: combines certified cloud for scalability and on-premise WORM storage for sovereignty.
Priority recommendations
- Implement a qualified timestamping service (TSA) integrated into the video capture chain.
- Adopt AES-256 GCM encryption from the edge device and secure transports with TLS 1.3.
- Deploy an immutable logging solution (private blockchain or Merkle tree).
- Conduct a comprehensive DPIA prior to any production deployment and maintain an up-to-date data retention policy.
- Implement robust IAM governance (MFA, RBAC, quarterly access reviews).
- Plan for resilience: geo-dispersed replication + monthly restoration tests.
References
[1] Autorité Nationale de Sécurité des Systèmes d'Information (ANSSI), Guide de la vidéosurveillance sécurisée, version 2.0, 2023, https://www.ssi.gouv.fr/guide/videosurveillance-securisee/, accessed 20 July 2026.
[2] European Union Agency for Cybersecurity (ENISA), Guidelines on Video Surveillance, 2022, https://www.enisa.europa.eu/publications/video-surveillance-guidelines, accessed 19 July 2026.
[3] Commission Nationale de l'Informatique et des Libertés (CNIL), Durée de conservation des images de vidéosurveillance, note technique n° 2021‑005, 2021, https://www.cnil.fr/fr/duree-conservation-images-videosurveillance, accessed 18 July 2026.
[4] European Union, eIDAS Regulation (EU) No 910/2014, consolidated text, 2023, https://eur-lex.europa.eu/legal-content/FR/TXT/?uri=CELEX%3A32014R0910, accessed 21 July 2026.
[5] National Institute of Standards and Technology (NIST), *Special Publication