Which policy applied to a supplier when its access was renewed last spring? Who approved it, based on what information and with what rights? The data is spread across the EDM system (electronic document management), the ERP, SIEM logs (security event management) and object storage. Answering requires linking records from systems that do not communicate and reconstructing their state at a date that was never fixed.
At StratoFoundry, we use two related terms for different things: Knowledge Layer and Memory Layer. Confusing them makes it harder to scope, manage and audit a layer that links information and a memory that preserves it over time.
The Knowledge Layer: linking what already exists
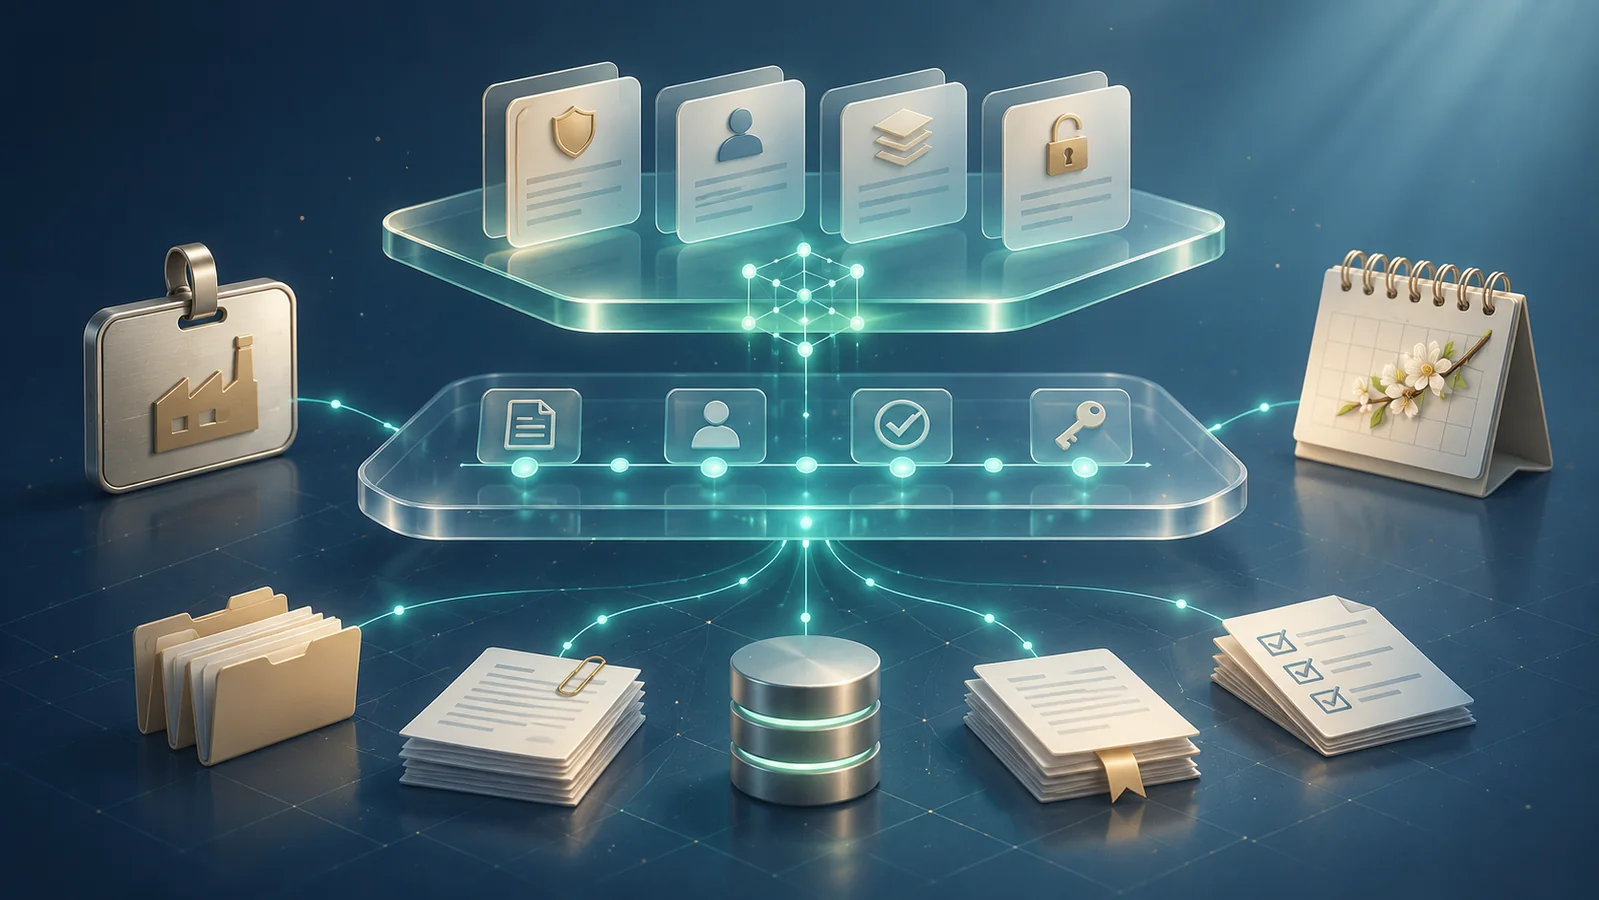
Let's start with the present. The Knowledge Layer is a cross-cutting layer that links objects, their successive states, their context and their evidence, without replacing the source systems. The EDM system stays the EDM system, the ERP stays the ERP, the backup stays the backup: each keeps its business authority, and the authoritative source remains the source of truth.
Four definitions are enough to clarify what 'linking' covers:
- A governed object is a logical entity tracked over time under explicit rules of identity, access, policy, provenance and integrity. A supplier contract, an AI model or a manufacturing batch can be one.
- A state is the set of attributes, relationships, metadata and references known for that object at a point in time or over an interval.
- Provenance captures the origin, the producer and the transformations of a piece of data or a state.
- A policy is a versioned rule applicable to an object, an actor, an access, an operation or a decision at a given time.
Two other terms change how a project is read. An evidence package is a structured dossier bringing together states, timeline, actors, policies, controls and known gaps: it supports an audit, without being either an audit or a certificate. And verifiable qualifies what is inspectable and checkable within a defined scope, not what would automatically be true, complete, compliant or certified.
Object storage, for its part, brings scale and configured retention. On its own, it brings neither persistent identity, nor operational context, nor governed history. The Knowledge Layer brings the rest.
The Memory Layer: what time adds
Linking is not enough. The Memory Layer refers to the value built over time, when this governed knowledge becomes queryable across time and reusable by several applications, users and agents.
The difference lies in looking back. The Knowledge Layer organizes what is linked now; the Memory Layer allows the question asked later: what was this object at a given date, which rules applied, which decision was made and on what basis. One formulation sums it up:
Useful data tells you what it contains. Governed data also lets you retrieve what it was, where it comes from, which rules applied, and what was done with it.
Reusability matters as much as time. The same governed history serves several uses without rebuilding a silo per use:
- Search: the right object, the right version, the right context.
- Evidence: demonstrable integrity, provenance, identity.
- Compliance: packaged controls, gaps and authorizations.
- Restoration: selection and verification of a trusted state.
Knowledge linked once then works for several teams, several applications, several years.
The supplier file, in three moments
Take a demonstration scenario, with fictional data. At T0, a supplier access renewal is approved: a 'medium risk' assessment at version 7, policy 3.2 in force, an active approval right, an AI model recommendation (renew for thirty days), a human validation captured at 9:12 am. The Knowledge Layer links all these pieces to the same governed object.
At T1, the state changes: the assessment moves to version 8, 'high risk', policy 3.3 becomes stricter, the right is revoked. The object's identity, however, does not move.
At T2, an incident triggers an investigation. The current state contradicts the past decision. Without captured history, that decision looks like a mistake. With it, it becomes readable again: legitimate given what was known, the rules then in force, and the rights of the person who validated it. The knowledge linked at T0 has become memory at T2, queryable across time and reusable by audit, security or procurement, without rebuilding the file three times.
Two boundaries not to erase
First boundary: verifiable does not mean certified. Integrity and provenance make a state inspectable; they do not prove its business truth, its completeness, its legality, or its compliance. An evidence package supports an audit or an assessment, it does not replace it. Confusing the two exposes you to two symmetrical risks: promising too much, or demanding from a tool what belongs to an auditor.
Second boundary: memory starts at T0, meaning when the scope is activated. KARL does not reconstruct a history that was never captured: only the objects, states and relationships captured within the governed scope are queryable. Activate the scope in January, and January becomes the start of memory, not the previous decade. This boundary gives the right reflex: define the scope that matters early, rather than regretting later a history nobody recorded.
Two terms, two realities. The Knowledge Layer is a linking effort, possible today on a chosen scope. The Memory Layer is a value that compounds: every week of capture adds to what you will be able to ask in a year. The architecture question that follows fits in one sentence: what is the first scope whose history you would regret not having in twelve months?
If this topic connects to a continuity problem at your organization (an audit to prepare, an investigation to make more reliable, knowledge that leaves with departing staff), let's start the conversation.